Quantifying Digital Executive Protection
Digital Executive Protection requires more than standard data broker removal. Discover the real incidents, the remediation, and the research behind the category, to build a program that genuinely protects your senior leaders.
Two Attacks Your Security Operations Would Never See
Fake merger and acquisition scams
Threat actors have been targeting organizations involved in merger or acquisition activities, posing as executives involved in the deal. In one case, a threat actor impersonated multiple contacts from different companies known to the intended victim. Conversations that started on WhatsApp were moved to personal email, and forged NDA documents were used to attempt acquisition fraud.
The attempt failed, but researchers later found four more incidents running the same playbook under different advisory brands. The entire attack lived on personal channels and corporate controls could not detect it.
See how BlackCloak helps executives confirm the authenticity of all communications on personal channels like WhatsApp.
When the data leaves the building
In January 2026, the Justice Department acknowledged in a court filing that DOGE personnel had accessed and shared sensitive Social Security data without agency officials’ knowledge, including through a third-party service that was not approved for that data. The Social Security Administration said it had not been able to determine exactly what data was shared or whether it still exists on that server.
Your executives’ most sensitive identifiers sit in systems neither you nor they control. Nobody can tell you for certain where they are now.
See how BlackCloak monitors, suppresses, and reduces executive exposure across the clear, deep, and dark web.
Faked to Perfection
Ponemon Institute surveyed U.S. security practitioners on deepfake readiness and identified why detection alone is far from sufficient.
Why Digital Executive Protection Is a Security Mandate
- 12x C-suite executives are more likely to be targeted in cyberattacks than other employees
- 75% of organizations reported an incident tied to a senior leader’s personal digital life in the last 12 months
- 8.7 staff hours consumed on average to remediate an incident originating in the personal lives of leadership
- 51% of security teams name a lack of visibility into personal environments as their biggest barrier
Source: Techstrong Research 2026, Ponemon Institute 2025.
Digital Executive Protection Use Cases
The Digital Executive Protection Framework
Discover the full range of use cases for Digital Executive Protection in the industry’s first standard, and cross reference against what you already have in place.
Four Clients, Four Problems, Four Outcomes
Case 1
Identity theft impacts an entire leadership team
Multiple senior leaders at a healthcare organization reported unemployment claims and small business loans were being taken out in their names. The volume of incidents experienced quickly overwhelmed their internal security and legal teams.
BlackCloak enrolled 14 members of the leadership team, running data broker removal and deep and dark web scanning for exposed passwords, before putting identity theft protection in place while remediating the outstanding fraud.
Case 2
Hijacked social account used to attack the company
A CxO at a manufacturing company with more than 2,000 employees had their personal social media account hijacked. Attackers used it to attempt money transfers and message employees directly. The security team needed to take back control without taking over the executive’s personal accounts.
BlackCloak contained the breach and onboarded the entire C-suite to our DEP Platform. The engagement went further than the incident itself, helping the CISO win buy-in for secure password vaults across the whole company.
Case 3
Executive data exfiltrated in a ransomware attack
A Life Sciences company was hit by a ransomware attack that exfiltrated the passport numbers, Social Security numbers, and passwords of its executive team and their assistants. The General Counsel accelerated a Digital Executive Protection project already in progress, covering executives and assistants with device security, home network scanning, deep and dark web monitoring, and identity theft protection.
Six months later, an executive’s personal social account was targeted. The attempt was detected and shut down immediately.
Case 4
Leaked intellectual property through personal devices
A pharmaceutical CISO had a 14-person executive team who occasionally used personal devices for company work. Attempts to extend corporate protections into executives’ personal lives met resistance. Then the team was hit with identity theft.
BlackCloak rolled out a Digital Executive Protection program using short onboarding sessions that kept executives in control of their own accounts. We secured their devices and remediated the identity theft, mitigating the risk of SEC disclosure.
Why Security Leaders Choose BlackCloak
-
Full-Category Coverage
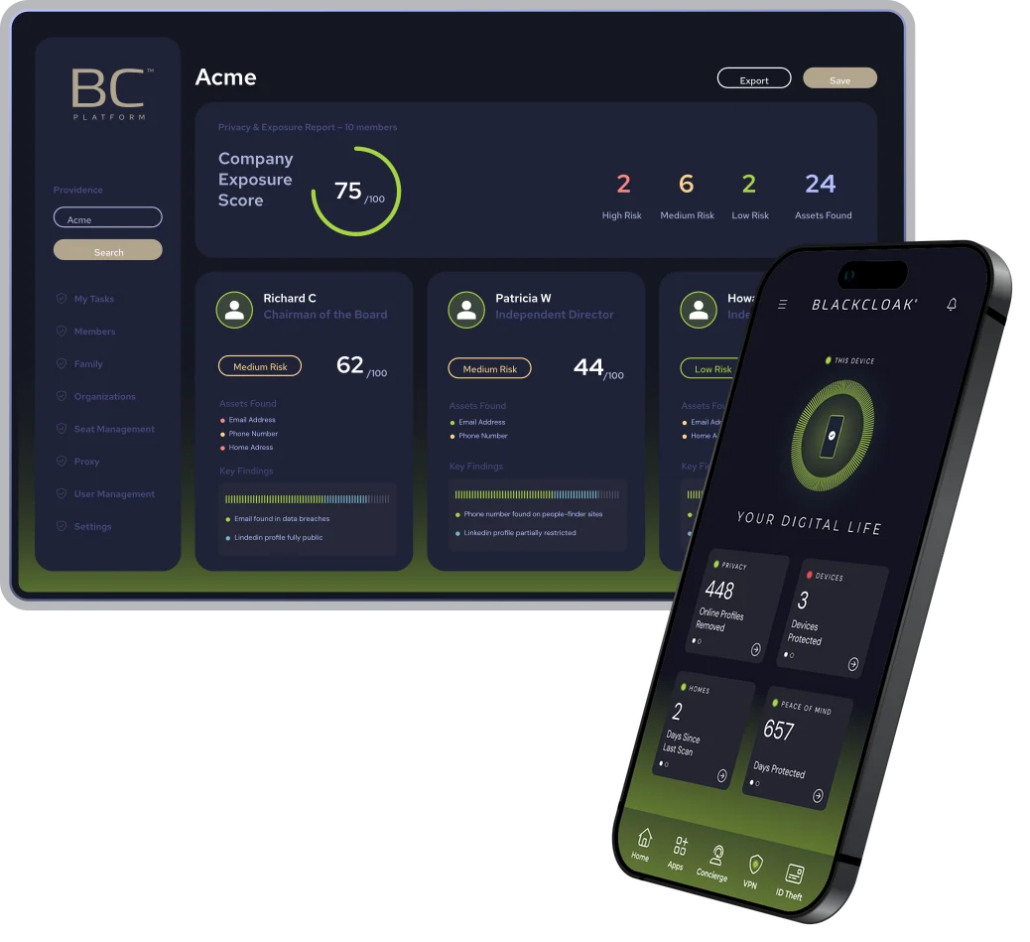
Competitors sell fragments of protection, such as data broker removal or device management. BlackCloak delivers the complete category in one platform, from one vendor, on one contract.
-
Zero Operational Burden
BlackCloak operates outside of your corporate cybersecurity technology stack. We take care of the execution and delivery of the program, providing regular reports to your team.
-
End-to-End Support
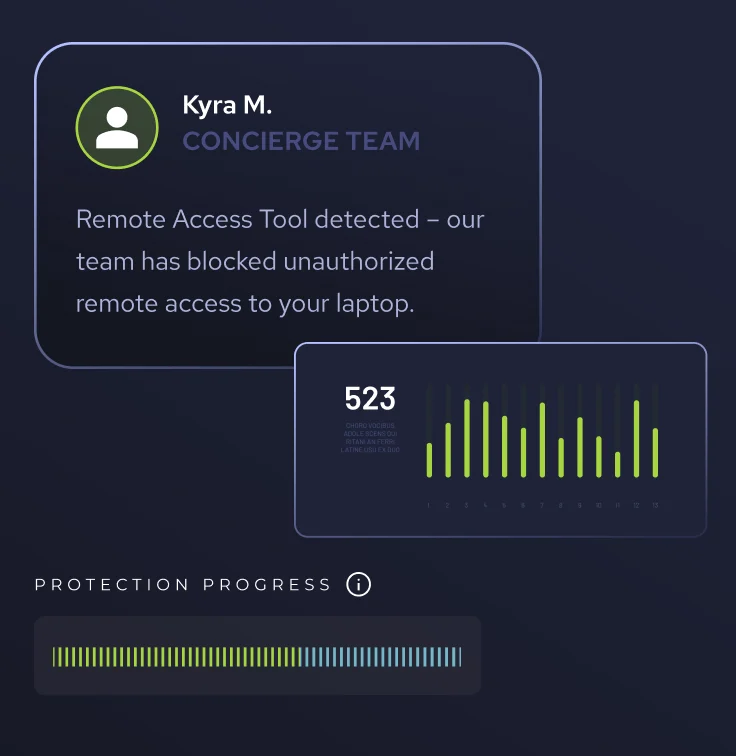
Many tools simply identify executive risk. BlackCloak owns the remediation, with our certified in-house US-based SOC who handle personal incident response from detection through to recovery.
-
A Privacy-First Approach
We manage executive personal environments privately. We do not share your executives’ data and we cannot see into their personal accounts or browsing history.
The Trusted Leader in Digital Executive Protection
I’ve seen first-hand how BlackCloak gives CISOs new levels of assurance they previously didn’t have. Their curated approach ensures executives’ personal cybersecurity is protected in ways not found elsewhere.
All cybersecurity professionals know that Digital Executive Protection is a major challenge. BlackCloak’s flexible and planned approach to protecting individuals – in all aspects of their lives – gives peace of mind to security teams and executives alike.
As a CEO I know I am a target for hacking and other attacks. Could hackers find out who we are, who my children were, watch our network, or even monitor financial information about my company? These are the types of things that keep me up at night, and BlackCloak has put those concerns to rest.
1 of 3
Research for security leaders
-
Report
Personal Exposure, Enterprise Risk
Techstrong quantifies the operational cost of executive incidents, including the 8.7 staff hours lost to remediate each one.
Read now Personal Exposure, Enterprise Risk -
Guide
Digital Executive Protection Framework
The first industry standard for safeguarding the personal digital lives of executives, built to help you structure and benchmark your program.
Read now Digital Executive Protection Framework -
Whitepaper
Faked to Perfection
Ponemon Institute surveyed US security practitioners on deepfake readiness and why detection alone is not enough.
Read now Faked to Perfection -
Article
The Dirty Secret of Data Broker Removal
Data brokers actively use tactics to make removing your executive’s info harder, but smart tech is breaking through.
Read now The Dirty Secret of Data Broker Removal
Protect Your Company By Protecting Your Executives
BlackCloak is trusted by Fortune 500 organizations to prevent personal cybersecurity incidents from reaching the corporate environment. Book a consultation to learn more about our comprehensive Digital Executive Protection Platform.